|
Getting your Trinity Audio player ready...
|
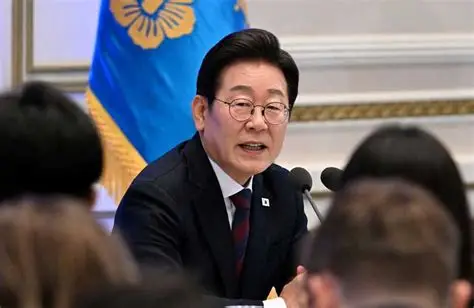
South Korea’s president has told his government to build defences that can spot and block cyber-attacks before they succeed, after a string of hacks exposed customer data at some of the country’s biggest banks. Speaking at a cabinet meeting on Tuesday, President Lee Jae Myung said AI models are believed to have been used in some of the recent incidents, and he asked for AI-driven security tools designed for that threat. The remarks have been summarized in some headlines as a call for tools that stop all attacks, but his actual request was narrower and more realistic: to detect threats early and block them in advance.
The immediate trigger was a wave of intrusions at financial firms. According to Reuters, South Korea’s Financial Services Commission said on Friday that Shinhan Bank, KB Kookmin Bank and others had reported cyberattacks, while the Yonhap news agency reported that Hana Bank and Woori Bank had also suffered breaches. The Korea Herald reported that customer information was exposed at seven companies, including Hana, KB Kookmin and Shinhan. Authorities have not yet disclosed the full scale of the breaches or what kind of AI tools were involved, so the extent of the damage remains unclear.
Lee’s language at the meeting was direct. He said signs of AI use have emerged in some of the hacking incidents, causing considerable public concern and anxiety, and asked officials to establish the circumstances swiftly and clearly, then concentrate personnel and resources on minimizing the harm. The Korea Herald reported that he also said it is difficult to answer evolving cyber threats by handling accidents after they happen, and that the country must have security capabilities able to detect and block attacks beforehand. He urged faster development and adoption of AI technologies tailored for cybersecurity and called for a complete overhaul of the nation’s security thinking to fit the AI era, according to The Register’s account.
Police have already moved. Yonhap, as relayed by Reuters, said officers launched a full-scale investigation into the attacks on commercial banks, and the Korea Herald said a 28-member team is examining possible violations of the information and communications network law. The president also called for vigilance across society and not only within government and the business sector, arguing that AI-driven hacking methods are widening the damage to previously unseen levels. The Register linked his words to earlier incidents such as the breach at the e-commerce firm Coupang, though that connection is the outlet’s reading and not a point the president spelled out.
The central idea behind his request is a shift from reaction to prevention. Traditional cybersecurity often begins after something has gone wrong, with a breach discovered, systems isolated, customers notified and lessons learned. Preemptive defence tries to catch the early signs, such as unusual login patterns, odd data transfers or the reconnaissance attackers perform before striking. Machine learning is well suited to spotting such patterns across huge volumes of activity, which is why governments and banks have invested in it. Lee’s call, in effect, is for South Korea to put those capabilities at the center of national policy and to share the work between public agencies and private companies, with The Register noting he wants collaboration to transform technology, systems and awareness.
Still, the headline version of the story deserves a caution. No tool can stop every cyber-attack, and security professionals say so plainly. Attackers need to succeed only once, while defenders must succeed every time, and AI helps both sides. The Register observed that the scope of the president’s demands is broad and that nobody believes cybercrime can be defeated outright. A realistic goal is to reduce the number of successful intrusions, shorten the time between break-in and detection, and limit how much data an intruder can take. Measured that way, AI defences can make a real difference, but they work best alongside basics such as patching, strong authentication, segmentation of networks and staff training.
The hacking itself raises a separate problem: how criminals use AI. Offensive uses reported across the industry include generating convincing phishing messages, writing or adapting malicious code, automating the search for vulnerabilities and imitating voices or identities. The South Korean authorities have not said which of these, if any, were involved in the bank incidents, and Lee himself spoke of signs and belief rather than confirmed findings. That uncertainty is important. Attributing an attack to AI is hard, and early statements by officials sometimes change as forensic work proceeds. Readers should treat the AI link as a claim under investigation.
For customers of the affected banks, the practical guidance is familiar. Watch account activity closely, be cautious about calls, texts and emails that mention the breach, since scammers often exploit news of a leak to impersonate banks, and use official channels to confirm any request for personal information or payment. If a bank advises changing passwords or replacing cards, do so promptly. These steps do not undo a leak, but they reduce the chance that stolen details are turned into fraud. The coverage reviewed does not describe what data was exposed at each bank, so customers should look to their own bank’s notice for specifics.
The episode also illustrates how quickly financial cybersecurity has become a matter of national policy. Banks hold the personal and financial details of most of a country’s population, and a successful attack can undermine trust well beyond the institutions involved. Lee’s decision to raise the issue at a cabinet meeting, and to ask for personnel and funding to be redirected, signals that the government sees the threat as more than a technical problem for individual companies. It also puts pressure on regulators and banks to show what they are doing, and on technology firms that supply security products to explain what they can deliver.
There are open questions about how the plan would work. Who pays for the new tools and who owns the data they analyze? How will privacy be protected if more monitoring is introduced? Can smaller financial firms, which often have fewer security staff, match the defenses of large banks? And how can the government measure progress when much of the activity is hidden? The president’s call sets a direction, but the details will be shaped by ministries, regulators and private companies in the coming weeks and months.
For countries elsewhere, including Nigeria, where banks and fintech firms face their own streams of fraud and intrusion attempts, the lesson is general rather than specific. Attackers are adopting automation, and defenders are being urged to do the same, while the fundamentals of good security still matter. Readers who follow technology and business developments in Nigeria and beyond can find more coverage at BusinessTech Nigeria. The cabinet remarks are reported in detail by the Korea Herald and, via Reuters, by The Japan Times.
Whether South Korea can turn a presidential directive into working defenses will depend on speed and coordination. For now, the government has set the goal: catch attacks earlier, respond faster and use the same class of technology that attackers are reported to be using.